
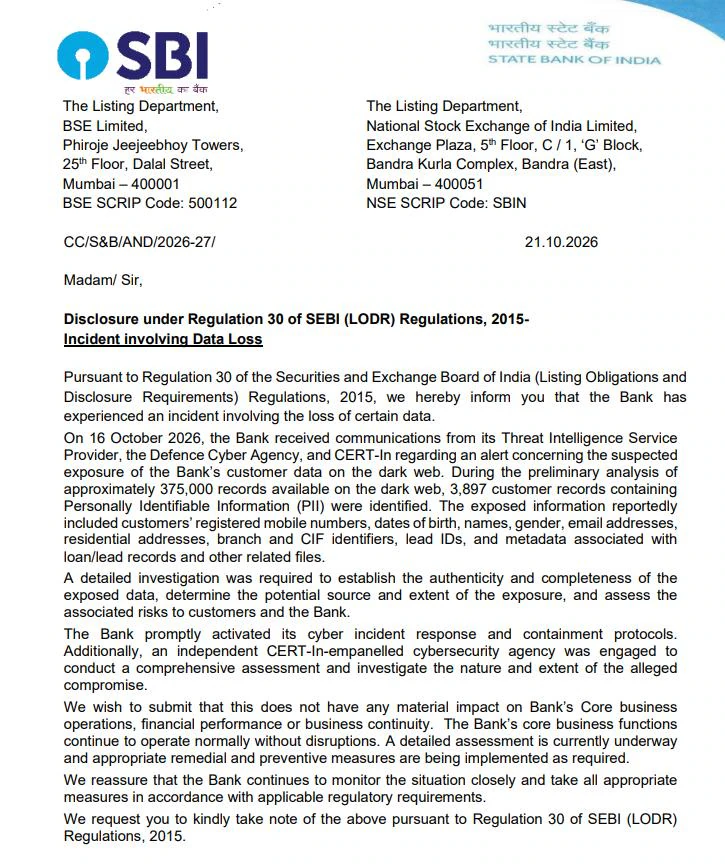
The State Bank of India (SBI) has confirmed a cyber incident involving the suspected exposure of customer information on the dark web. The bank identified 3,897 customer records containing personally identifiable information during its preliminary investigation. The exposed data reportedly included names, registered mobile numbers, dates of birth, email addresses and residential addresses. The records also contained customer identification details and information linked to loan applications. SBI clarified that the incident had not disrupted its core banking operations or business continuity. The bank has launched an investigation to determine the source and extent of the exposure.
SBI Investigates Exposure of 3,897 Customer Records
On October 16, SBI received alerts from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In). These alerts warned the bank about the suspected exposure of customer information. Following the alerts, SBI began examining the available data to assess the potential impact. The bank reviewed approximately 375,000 records discovered on the dark web. Its preliminary analysis identified 3,897 records containing sensitive customer information. SBI stated that investigators must conduct further checks to establish the authenticity and completeness of the exposed records.
The exposed information reportedly included several categories of personal and banking-related data. These details included customers’ names, registered mobile numbers, dates of birth, gender, email addresses and residential addresses. The records also contained branch identifiers, Customer Information File (CIF) numbers and lead identification numbers. Additionally, investigators found metadata associated with loan applications, customer leads and related files. Such information could create privacy and security risks if criminals misuse it. However, SBI has not yet confirmed the full extent of the exposure or whether every identified record contains authentic and complete customer information.
Also Read : UP Shock: Two Saints Murdered, Bodies Burnt Inside Shahjahanpur Temple
Bank Assures Customers as Core Banking Services Remain Unaffected
SBI has reassured customers that the incident has not affected its core banking services. The bank stated that its essential business functions continue to operate normally without disruption. It also activated its cyber incident response and containment procedures after receiving the alerts. SBI is investigating the possible source of the exposed information and assessing the potential risks to customers and the institution. The bank has also committed to monitoring the situation and taking appropriate measures in line with applicable regulatory requirements. SBI has not publicly identified the individuals or group responsible for the incident.
The incident follows claims by an anonymous hacker group identified as Siriusim, which reportedly alleged that it had obtained information relating to approximately 375,000 SBI customers. The group allegedly posted its claims on the dark web forum BreachForums. However, SBI has not confirmed the identity of the alleged attackers or established whether the claims accurately describe the incident. The case also highlights growing cybersecurity concerns across India’s banking sector. In July, Bank of Baroda acknowledged a data leak reportedly involving around one terabyte of customer data. These incidents underline the importance of stronger data protection, continuous monitoring and rapid incident response across financial institutions.